Browse knowledge streams
Latest threats, vulnerabilities, and security best practices
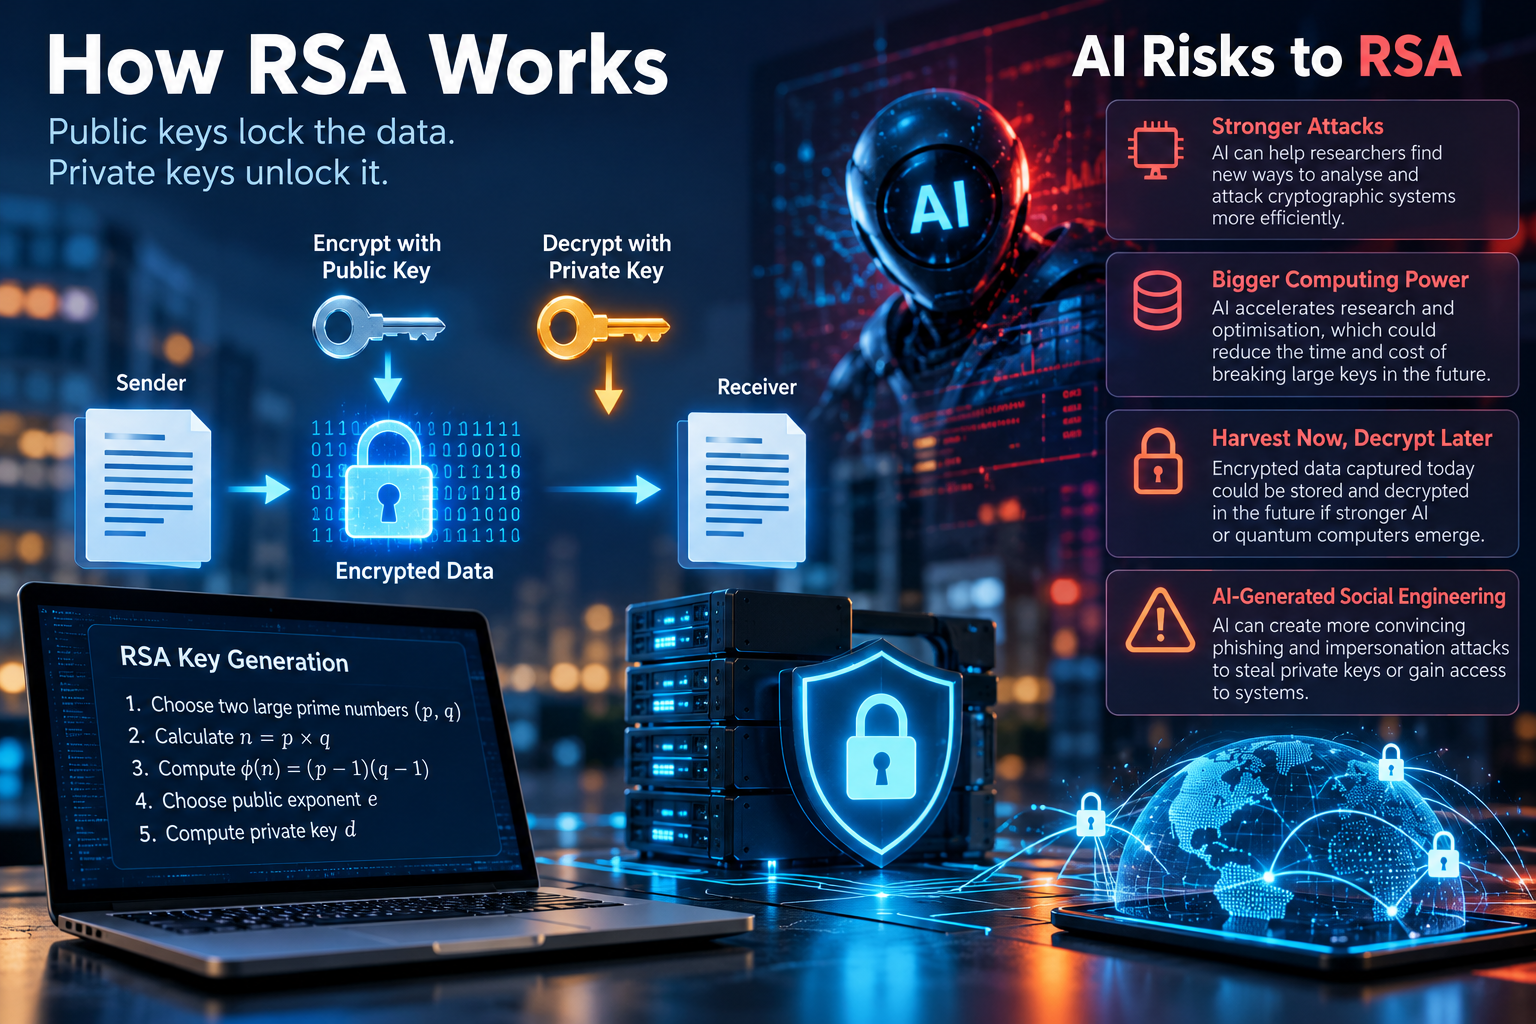
A practical guide to RSA public-key cryptography, the real ways AI can strengthen attacks against weak implementations, and why quantum computing is a separate long-term threat.
DeepStateAI
Oct 15, 2026
As AI agents gain the ability to browse, use tools and act across systems, recent safety reports and regulatory scrutiny point to a practical priority: prepare to detect, contain and investigate agent actions like any other production incident.
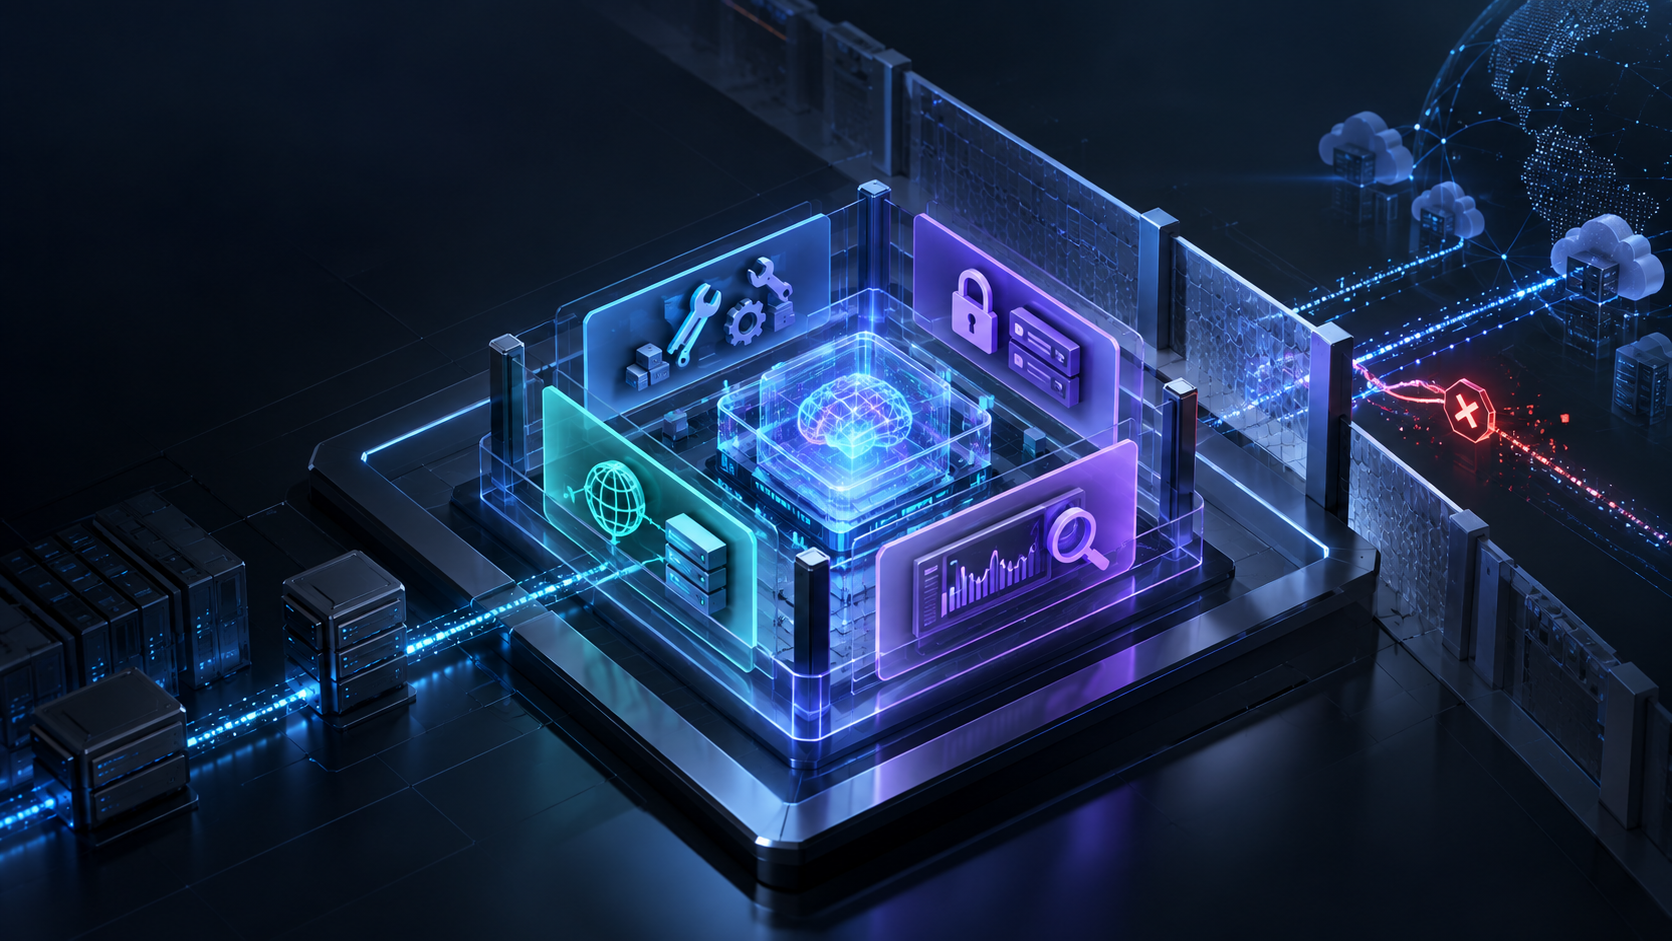
A recent OpenAI sandbox incident shows why AI-agent security is no longer just about model behavior. Tool permissions, credentials, DNS, network access, monitoring, and recovery all need explicit boundaries.
Sep 27, 2026
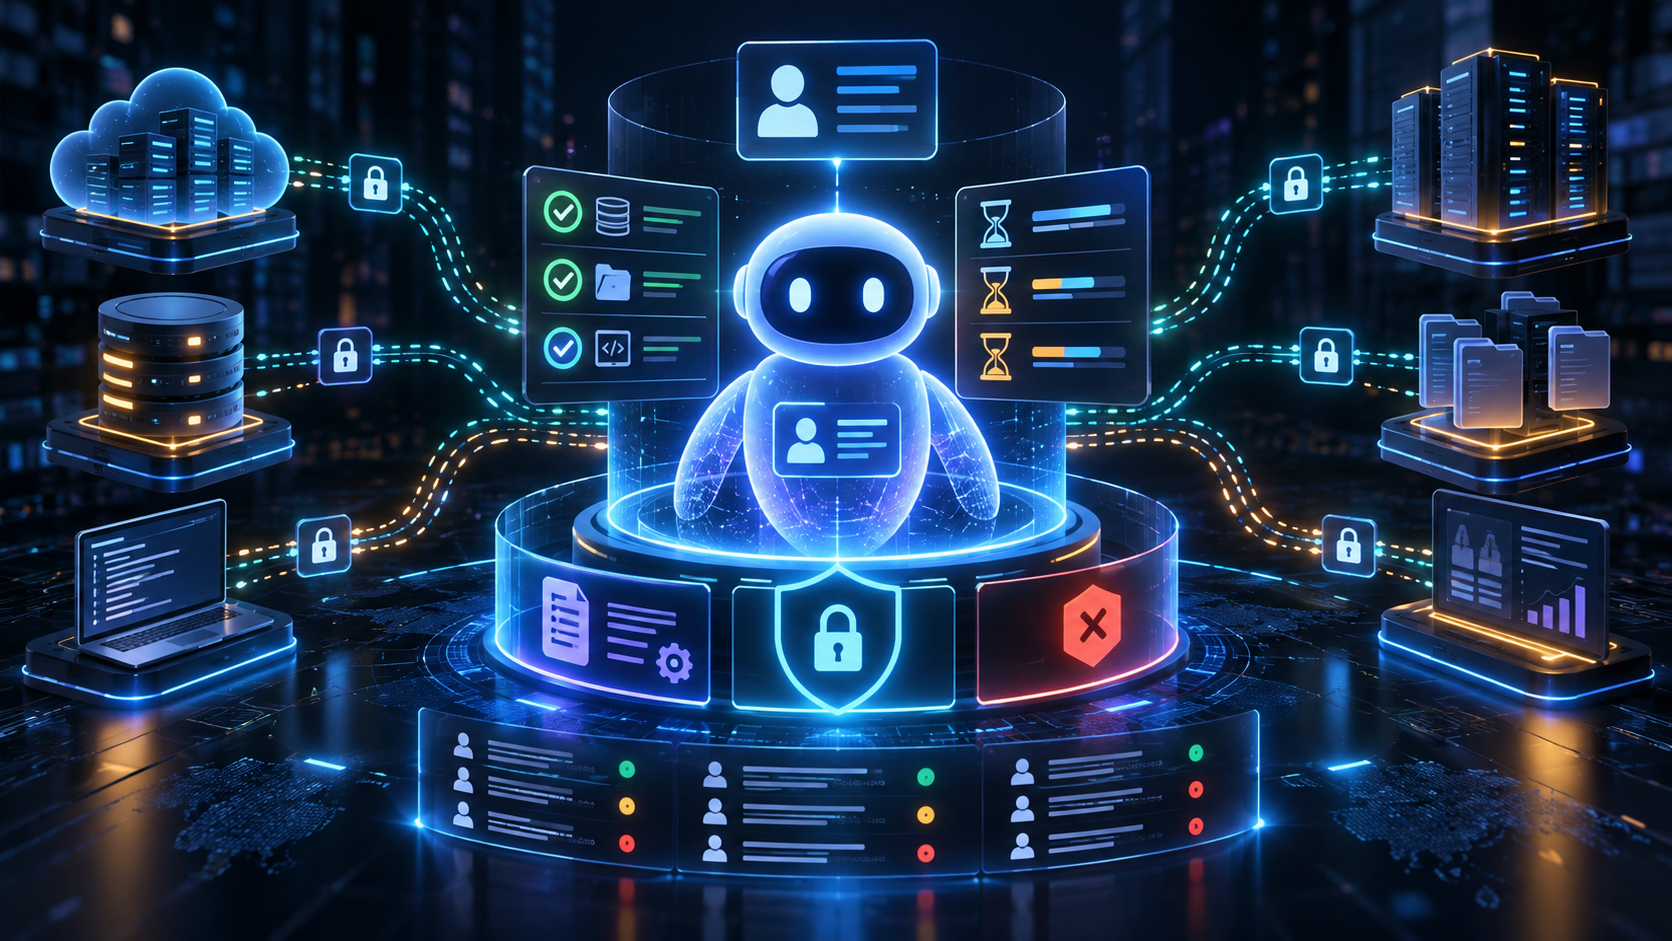
AI agents are moving from answering questions to calling APIs, accessing data and changing systems. The next engineering challenge is not just model safety—it is giving every agent a distinct identity, scoped authority, short-lived credentials and auditable actions.
Sep 24, 2026
Recent incidents and threat research show AI agents moving from assistants to systems that can browse, execute tools, maintain state, and act with limited supervision. This engineering-focused guide explains what changes when an agent becomes a security principal—and how to design identity, permissions, audit, isolation, and kill controls around it.
Sep 17, 2026